
Tech
What Is DDoS Protection, and Why Are DDoS Mitigation Services Moving to the Network Edge?

Key Takeaways
|
What is DDoS protection?
DDoS protection refers to the tools and techniques used to detect and stop distributed denial-of-service attacks, in which an attacker floods a website, application, or network with so much junk traffic that real users can no longer get through. Modern DDoS protection works in layers: some tools handle massive volumetric floods at the network level, others watch for smaller, more targeted attacks aimed at a specific application, and the strongest setups combine on-premises appliances, cloud-based scrubbing, and, increasingly, protection built directly into the network edge.
The stakes for getting this right keep rising. A successful attack does not just take a website offline for a few minutes; it can knock out APIs and applications that a business, or its customers, depend on for hours at a time, translating directly into lost revenue and, often just as damaging, a lasting hit to customer trust. In sectors like finance, healthcare, and telecommunications, where customers expect near-absolute service availability, even a single well-publicized outage can send business to a competitor.
What does layered DDoS protection actually look like in practice?
Rather than a single tool or appliance, effective DDoS protection is really a set of coordinated capabilities working together, each covering a different stage of an attack:
- Monitoring and baselines: the system continuously learns what normal traffic looks like, so it can flag a suspicious surge or anomaly quickly, rather than relying on static thresholds alone.
- Threat detection: deep packet inspection and behavioral analytics identify known DDoS patterns, such as SYN floods and botnet activity, alongside subtler, never-seen-before anomalies.
- Real-time mitigation: once a threat is confirmed, the system applies rate limiting and traffic filtering, and, where needed, routes traffic through a scrubbing center to remove malicious packets.
- Adaptive defense: as an attack evolves, for example shifting from a network-layer flood to an application-layer assault, the protection adjusts to block the new vector without losing legitimate traffic.
Why are DDoS attacks becoming harder to stop?
Attack volumes are not just growing, they are compounding. Cloudflare’s Q4 2025 DDoS Threat Report found that DDoS attacks surged 121% year over year in 2025, with the total number of attacks more than doubling to 47.1 million and telecommunications providers emerging as the most targeted industry. Network-layer attacks specifically nearly tripled, rising from 11.4 million in 2024 to 34.4 million in 2025, and the same report recorded a new record: a 31.4 Tbps attack that lasted just 35 seconds.
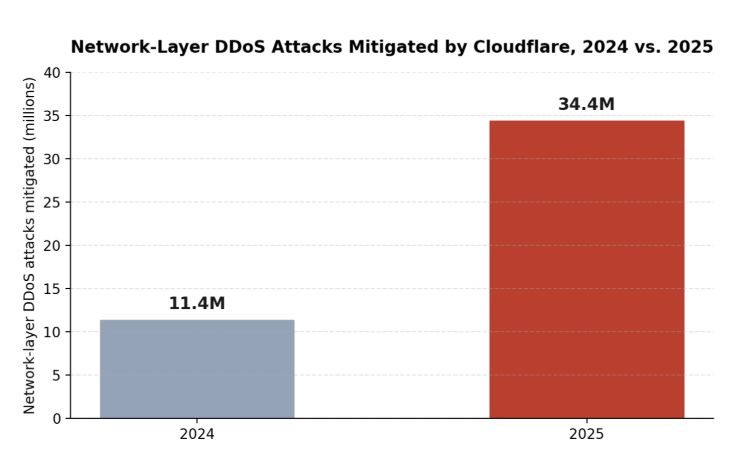
Network-layer DDoS attacks mitigated by Cloudflare, 2024 versus 2025.
That kind of growth changes the calculus for anyone running a network. A defense sized for last year’s attack volumes can be overwhelmed by this year’s, which is part of why so many DDoS mitigation services are being redesigned around detecting and blocking attacks closer to where they start, rather than waiting for traffic to reach a centralized location.
What are the limits of traditional, centralized DDoS mitigation services?
Conventional DDoS protection solutions typically rely on centralized, cloud or data center based mitigation: when an attack is detected, traffic gets rerouted to a scrubbing center that filters out malicious packets before forwarding the rest along. An overview of where conventional DDoS protection solutions leave security gaps points out that while this approach can handle large volumetric floods, it has some real blind spots. Rerouting adds latency, since all traffic, malicious or not, has to travel through a distant mitigation point, and short-lived or low-volume attacks may never trigger the thresholds needed to kick off scrubbing in the first place.
There is also a structural gap worth calling out: scrubbing centers generally operate at Layer 3, filtering routed IP traffic. If a connection runs over Layer 2, direct, non-routed links, it can bypass that inspection layer entirely, leaving a real exposure gap for the kind of point-to-point and peering connections that carry a lot of service provider and enterprise traffic.
How does edge-based DDoS protection close those gaps?
Rather than hauling all traffic back to one place, edge-based DDoS protection distributes detection and mitigation out to the edge of the network, at customer premises equipment, provider edge routers, Layer 2 interconnects, and peering points. A use case covering DDoS protection deployed directly at the network edge walks through how this lets malicious traffic get identified and filtered within seconds, right where it enters or leaves the network, without rerouting legitimate traffic off its normal path. That matters operationally: no added latency for real users, no new single point of failure, and a defense that scales naturally as a provider adds more edge devices or customer sites.
What role does AI play in modern DDoS mitigation services?
AI and machine learning have become central to how DDoS protection solutions actually distinguish an attack from a legitimate traffic spike, like a flash sale or a viral moment, in real time. Edge-deployed threat intelligence, such as a software-based DDoS protection solution designed to run on existing network hardware, analyzes traffic patterns locally and can catch both known attack signatures and zero-day anomalies, including multi-vector “orchestration” attacks that blend several techniques at once. Because the detection logic runs on hardware that is already deployed, this kind of DDoS mitigation service can be added without a costly infrastructure overhaul, and service providers can package it as a managed offering for their business customers.
Can DDoS protection stop outbound attacks too?
It is easy to think about DDoS protection purely as a shield against incoming floods, but a compromised device inside a network, one caught up in a botnet, can just as easily become a source of outbound attack traffic against someone else. Effective DDoS protection solutions monitor traffic in both directions, so a hijacked device attempting to join an attack gets caught and blocked at the edge before it can damage the provider’s own reputation or its downstream customers. This two-way coverage matters increasingly for service providers, since being identified as the unwitting source of an attack can carry its own reputational and even contractual consequences with upstream partners.
What should a network operator look for in a modern DDoS mitigation service?
Not every DDoS mitigation service is built the same way, and the differences tend to show up most under real attack conditions rather than in a product brochure. A few practical questions are worth asking before committing to one:
- Does it protect Layer 2 as well as Layer 3 traffic, or only routed IP connections that pass through a scrubbing center?
- How quickly does it detect and mitigate an attack, seconds, minutes, or only after a threshold-based alert fires and a human intervenes?
- Does it require dedicated hardware, or can it run on network edge equipment that is already deployed?
- Can it be offered as a managed service, so a communications service provider can extend DDoS protection to its own business customers as a value-added offering rather than a one-off project?
Frequently Asked Questions
What’s the difference between DDoS protection and DDoS mitigation?
The terms are often used interchangeably, but DDoS protection typically refers to the full set of tools and practices used to prevent and defend against attacks, while DDoS mitigation describes the specific act of detecting and neutralizing an attack once it starts.
Why do centralized DDoS mitigation services add latency?
Because all traffic, malicious or not, has to be rerouted through a scrubbing center before it reaches its destination, adding a hop, and distance, that edge-based approaches are designed to avoid.
Can DDoS protection be added to a network without replacing existing equipment?
Yes. Software-based DDoS protection solutions can run on network edge equipment that is already deployed, which is part of why they can be rolled out as a managed service without a hardware refresh.
Do small, short-lived DDoS attacks matter if they don’t cause an outage?
They can still cause real damage. Traditional mitigation is often tuned to catch large volumetric floods, so short or low-volume attacks can slip past detection thresholds entirely, which is one of the main gaps that edge-based DDoS protection is designed to close.

Key Takeaways
|
What is shadow AI, exactly?
Shadow AI is what happens when employees adopt AI tools, applications, or agents on their own, without going through IT approval or a security review. It looks different depending on where you find it: a browser-based chatbot an employee uses for drafting emails, an AI coding assistant a developer installed without asking, a spreadsheet plugin that quietly calls out to a language model, or a workflow automation an operations team stitched together over a weekend. None of it is necessarily malicious. Most of it exists because it made someone’s job easier, faster than waiting on a formal procurement or approval process.
Why does shadow AI spread so fast inside organizations?
Shadow AI spreads fast, hides easily, and most enterprises don’t even realize how widespread it has become. Ovalix’s own analysis of this problem frames it plainly: AI adoption is accelerating everywhere at once, marketing teams use GenAI to create content, developers rely on code assistants, finance experiments with AI-driven analytics, and somewhere in the organization an employee is very likely pasting sensitive data into a public AI tool without IT knowing. AI adoption keeps accelerating while security frameworks struggle to keep pace, and shadow AI is the predictable result of that gap.
How big is the shadow AI problem becoming?
The scale of the issue is starting to show up in market data, not just anecdotes. MarketsandMarkets’ shadow AI risk and governance market research estimates the category reached roughly $285 million in 2025 and projects it will climb to $3.485 billion by 2032, a compound annual growth rate of approximately 43%, among the fastest-growing segments of the broader AI governance market. That kind of growth rate reflects how quickly organizations are recognizing shadow AI as a distinct, budget-worthy problem rather than a footnote inside general IT security.
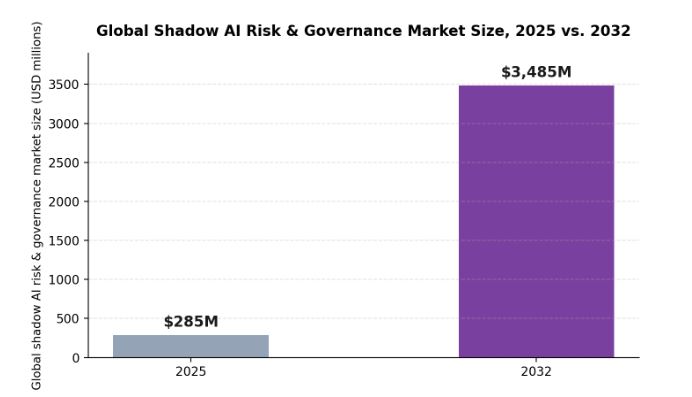
Global shadow AI risk and governance market size, 2025 versus 2032, according to MarketsandMarkets.
What is AI-SPM, and how is it different from ordinary shadow IT discovery?
AI Security Posture Management (AI-SPM) is the category that emerged specifically to help organizations understand and secure their fast-growing AI ecosystems, starting with the same basic question traditional shadow IT discovery asks, but applied to a much more dynamic and fast-moving category of software. Before you can detect threats, enforce policy, or govern AI usage, you need to know which AI systems actually exist in your environment, and that inventory has to be broader than most teams initially expect.
| What AI-SPM has to discover | Why it’s easy to miss |
|---|---|
| Public AI applications used across departments | Adopted independently by individual teams, often through a browser extension or free-tier signup. |
| Homegrown AI systems built internally | Developed by teams outside security’s normal software inventory process. |
| AI agents running autonomous workflows | Often configured once and left running, with no ongoing review of what they can access. |
| Embedded AI features inside business systems | Bundled into SaaS tools the organization already approved for other reasons. |
| AI code assistants used by developers | Installed at the individual developer level, frequently outside standard software approval. |
What does a complete AI-SPM program actually require?
- Continuous discovery, not a one-time audit: AI adoption grows daily, so a snapshot inventory is out of date almost as soon as it’s compiled.
- Visibility into prompts and data flows: knowing an AI tool exists isn’t enough; understanding what data moves through it matters just as much.
- Policy enforcement, not just reporting: discovery on its own doesn’t stop a data leak; it has to connect to real controls.
- Coverage across sanctioned and unsanctioned tools alike: approved AI applications still need monitoring, since approval doesn’t guarantee safe usage.
Ovalix’s public AI application security product is built around exactly this combination: continuous discovery of unauthorized AI tools and usage, end-to-end visibility into user requests, model responses, and data flows within both sanctioned and unsanctioned AI apps, and enforcement that blocks unsafe requests and prevents data exposure before it happens, rather than only reporting on it after the fact.
How does closing the discovery gap change what’s possible next?
Once an organization can actually see its full AI footprint, the conversation shifts from “what don’t we know” to “what do we do about what we found.” That’s the point at which policy enforcement, data protection controls, and compliance mapping become realistic rather than aspirational, because they can finally be applied against a complete picture instead of the partial one most security teams have been working from. Closing the discovery gap doesn’t eliminate AI risk on its own, but it is the precondition every other AI security control depends on.
Frequently Asked Questions
Is shadow AI always a sign of a security failure?
Not necessarily. Shadow AI usually reflects a gap between how fast employees want to adopt useful tools and how fast formal approval processes can keep up, rather than deliberate rule-breaking. The security failure, if there is one, is usually a lack of visibility rather than malicious intent.
Can a one-time audit find all the shadow AI in an organization?
No. AI adoption changes daily as new tools launch and employees find new ways to use existing ones, so a point-in-time audit is typically out of date within weeks. Effective AI-SPM relies on continuous discovery rather than a periodic snapshot.
Does AI-SPM only cover public AI tools like chatbots?
No. A complete AI-SPM program covers public AI applications, homegrown internal AI systems, AI agents running autonomous workflows, embedded AI features inside other business software, and AI code assistants used by developers.
What’s the difference between AI-SPM and general shadow IT management?
AI-SPM applies the same discovery-first logic as shadow IT management, but is built specifically for how AI tools behave: it needs visibility into prompts, model responses, and data flows, not just which application is installed or which account exists.
| Key Takeaways
• The global microcatheter market is projected to grow from about $874 million in 2023 to roughly $1.14 billion by 2028, a compound annual growth rate near 5.5 percent. • A coil generally must measure under 0.8 millimeters in diameter to be inserted into a vein, which requires purpose-built winding machinery rather than off-the-shelf equipment. • ISO 13485:2016 sets quality management requirements covering design, production, installation, and servicing for organizations that manufacture medical devices. • Some manufacturers now wind coils with more than 1,000 turns into a form smaller than the head of a pin for use in ablation and drug-delivery catheters. |
What size coil is needed for a catheter-based medical device?
A coil generally needs to measure under 0.8 millimeters in diameter to be inserted into a vein, which rules out standard commercial coil-winding equipment and requires purpose-built winding machinery designed for that scale. how manufacturers wind coils thin enough to fit inside a 0.8 mm vein walks through why this level of miniaturization changes the manufacturing process itself, not just the finished part, since tension control, wire handling, and core-forming all behave differently at sub-millimeter scale.
How is a coil for a catheter or drug-delivery device actually manufactured?
A coil for this kind of device is wound from insulated wire, sometimes with more than a thousand turns, onto a form small enough to be smaller than the head of a pin, then connected to lead wires without damaging the ultra-fine winding. coil designs used across ablation and drug-delivery catheters shows the range of shapes involved, including cylindrical, elliptical, ball-shaped, and multi-layer coils, each suited to different catheter geometries and clinical applications such as cardiac ablation, targeted drug delivery, and diagnostic sensing. Choosing among those shapes is rarely just an electrical decision, since a coil’s physical geometry also affects how flexible the finished catheter segment is, how it responds when advanced through a curved vessel, and how much space remains for any other lead wires or lumens running alongside it.
How big is the market for catheter-based devices that rely on these coils?
a third-party market research report on microcatheters projects the global microcatheter market to grow from about $874 million in 2023 to roughly $1.14 billion by 2028, a compound annual growth rate of around 5.5 percent. The same research found that single-lumen microcatheters account for the largest share of that market, at approximately 91.7 percent, reflecting how much of this growth is concentrated in relatively simple, high-volume catheter designs rather than complex multi-lumen devices. That volume matters for sourcing decisions: a coil manufacturing partner needs to be able to scale from prototype quantities to steady production without requalifying the process each time.
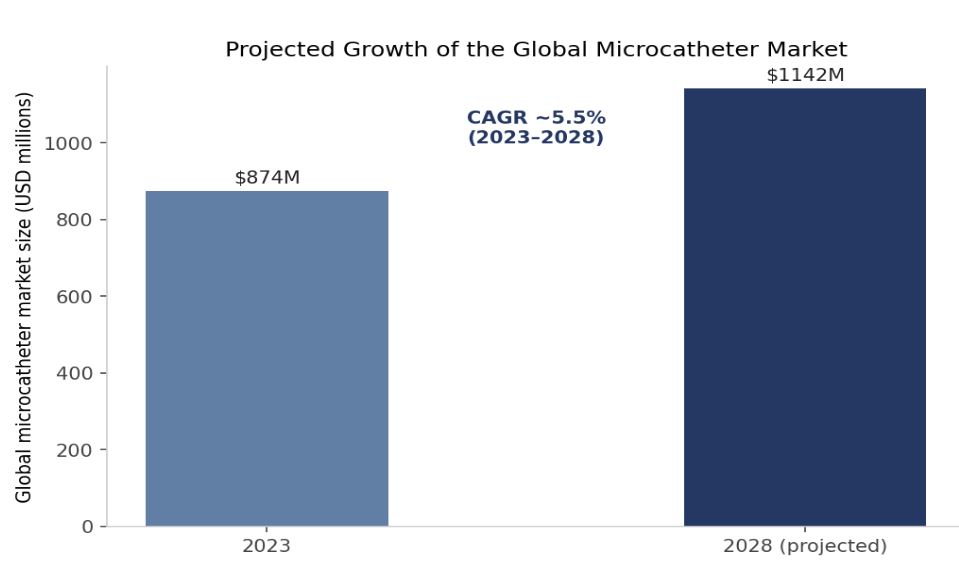
Projected global market size for microcatheters, 2023 versus a 2028 forecast, based on third-party market research.
What quality certifications should a coil manufacturing partner hold?
A coil manufacturing partner supplying catheter-based medical devices should hold ISO 13485:2016 certification, which sets quality management requirements covering design, production, installation, and servicing specifically for medical device manufacturers. the ISO certifications that govern medical-grade coil production lists the specific certifications relevant to coil production, since general ISO 9001 quality management and medical-specific ISO 13485 certification are both worth confirming before committing to a supplier. These certifications exist because risk management and regulatory traceability matter more once a component ends up inside a patient rather than inside a piece of industrial equipment.
What information should a developer share with a coil manufacturer before starting a project?
A developer should be ready to share the target coil dimensions, the electrical performance the coil needs to deliver (such as inductance or turns count), the catheter or device geometry it has to fit inside, and any sterilization or biocompatibility requirements the finished assembly must meet. It also helps to share where the project sits in its development timeline, since a manufacturing partner capable of small prototype runs for design validation is not automatically the same partner best suited to scaling a validated design into steady commercial production. Being upfront about volume expectations early tends to avoid a costly requalification cycle later, particularly for a medical coil supplier whose winding and bonding process may need formal validation under design controls before volume production begins.
Why does lead time differ so much between a coil prototype and a production order?
A handful of prototype coils can often be hand-wound or produced on flexible lab equipment within days to a couple of weeks, while a validated production run generally requires a qualified, repeatable process running on dedicated tooling, which takes considerably longer to set up the first time. That gap catches some device teams off guard late in development, when a design that worked perfectly as a prototype needs to move into steady, auditable production under design controls before a regulatory submission can proceed. Asking a prospective coil manufacturing partner to walk through their prototype-to-production transition process, not just their prototype turnaround time, is one of the more reliable ways to avoid a schedule surprise later in the project.
What else should a device developer ask before choosing a coil manufacturing partner?
Beyond certifications, a device developer should ask how thin a wire the partner can reliably wind and connect, since that number effectively caps how far a catheter design can be miniaturized. the winding techniques behind sub-millimeter medical coils is a useful reference point for the kind of winding and connection detail worth asking a prospective supplier to walk through directly, including how they join fine wire without introducing heat damage or strain at the joint.
How does the choice of coil manufacturing partner affect a regulatory submission?
A regulatory submission for a catheter-based device typically needs documented evidence that the manufacturing process is controlled and repeatable, which means a coil supplier’s own quality system becomes part of the device maker’s overall design history and risk file, not a separate concern. Switching coil suppliers after a design has already been validated can trigger a formal change control and re-verification process, since even a nominally identical coil produced on different equipment or by a different process may behave differently at the tolerances involved in sub-millimeter winding. That is part of why device developers tend to weigh manufacturing stability and quality documentation as heavily as price when choosing a coil supplier, rather than treating it as a purely transactional sourcing decision.
Frequently Asked Questions
What size does a coil need to be to fit inside a catheter for vein insertion?
A coil generally needs to measure under 0.8 millimeters in diameter to be inserted into a vein, which requires specialized winding equipment rather than standard commercial coil-winding machinery.
How fast is the microcatheter market growing?
Third-party market research projects the global microcatheter market to grow from about $874 million in 2023 to roughly $1.14 billion by 2028, a compound annual growth rate of around 5.5 percent.
What does ISO 13485 certification mean for a coil manufacturer?
ISO 13485:2016 is a quality management standard that sets requirements for the design, production, installation, and servicing of medical devices, covering risk management and regulatory compliance throughout the product lifecycle.
Why do catheter-based devices need custom-wound coils instead of standard ones?
Catheter-based devices often require coils with hundreds or over a thousand turns packed into a diameter smaller than a pinhead, a level of miniaturization that generally requires purpose-built winding machinery rather than off-the-shelf coil production lines.
| Key Takeaways
• Companies must register with Brazil’s RADAR system through Receita Federal before they can import goods, and eligibility depends on an active CNPJ, compliant company stakeholders, and an Electronic Tax Domicile on file. • RADAR assigns one of three operating modalities automatically based on estimated financial capacity: Limitada tiers capped at US$50,000 or US$150,000, or Ilimitada for unrestricted operations. • Telecom equipment entering Brazil must now carry ANATEL certification numbers inside the country’s Single Import Declaration (DUIMP), under a rule ANATEL implemented via Ato No. 18086, effective May 25, 2026. • Brazilian customs routes import declarations into one of four inspection channels — Green, Yellow, Red, or Gray — with Gray reserved for shipments suspected of fraud or under-invoicing. |
What has to happen before a shipment can even be filed with Brazilian customs?
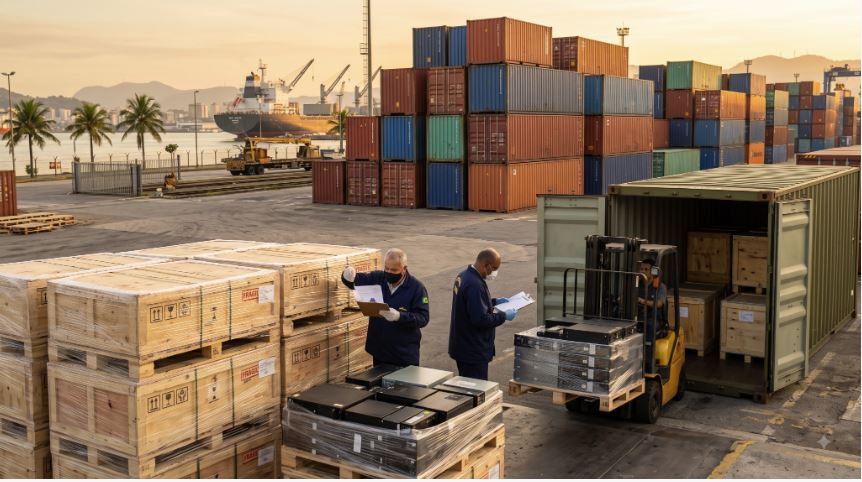
Before any shipment can be filed, the importing company has to be registered with RADAR, Brazil’s own import-operator registration system, managed by Receita Federal, the country’s federal tax authority. Eligibility depends on holding an active CNPJ (company registration number), adopting an Electronic Tax Domicile, and having stakeholders with regular or pending-regularization tax status; a company with prior suspensions or cancellations on file can be disqualified outright. a full walkthrough of Brazil’s import compliance process for tech shipments covers what that registration step looks like in practice alongside the rest of the customs process.
What are the actual steps once a shipment reaches a Brazilian port?
Once RADAR registration is in place, a shipment moves through eight sequential steps: pre-import preparation and licensing, product classification under the correct HS/NCM code, documentation preparation, filing the Import Declaration through Brazil’s SISCOMEX electronic system, assignment to an inspection channel, duty and tax payment, release to free circulation, and potential post-clearance audit of the declared values.
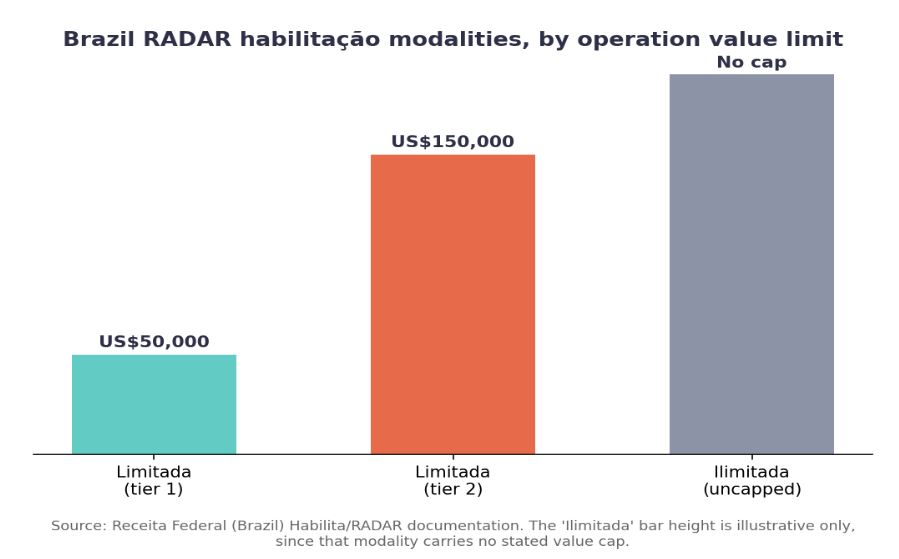
RADAR habilitação modalities and their operation-value limits. The Ilimitada bar is illustrative only, since that modality carries no stated value cap.
What determines which RADAR modality a company is assigned?
RADAR’s Sistema Habilita assigns one of three modalities automatically, based on the company’s estimated financial capacity rather than a manual application choice: Expressa, restricted to public corporations; Limitada, capped at either US$50,000 or US$150,000 in operation value; or Ilimitada, for unrestricted operations. A company that underestimates its own shipment volume can find itself capped at a lower tier than its actual import program needs.
What changed for telecom equipment specifically in 2026?
Brazil’s National Telecommunications Agency, ANATEL, implemented an update effective May 25, 2026 under Ato No. 18086 that requires ANATEL certification numbers to be included directly in Brazil’s Single Import Declaration (DUIMP) customs documentation. the U.S. government’s own summary of that change notes that ANATEL’s certification database is now integrating with SISCOMEX so customs can flag discrepancies during clearance, and that a related rule, Resolution No. 780/2025, expanded homologation obligations and liability exposure to online marketplaces as well as traditional importers.
Which taxes actually apply to an IT hardware shipment landing in Brazil?
- Import Duty (II) — the base federal import tariff
- Industrialized Product Tax (IPI) — applied to manufactured goods, including most IT hardware
- PIS/COFINS — federal social-contribution taxes calculated on the import transaction
- ICMS — a state-level value-added tax whose rate varies by the state of entry
Does the process look the same everywhere in Latin America?
No, RADAR, SISCOMEX, and ANATEL are specifically Brazilian systems, and neighboring countries run their own registration and certification regimes even when the underlying documents, like commercial invoices and certificates of origin, look similar on paper. regional logistics coverage across Latin American markets and a comparable process breakdown for neighboring Argentina are useful side-by-side references for a company shipping into more than one Latin American market at once.
Frequently Asked Questions
What is RADAR and why does a company need it before importing into Brazil?
RADAR is the registration a company must hold with Brazil’s Receita Federal before it can file import operations through SISCOMEX, and it determines the maximum value of goods that company is authorized to import based on automatically calculated financial capacity.
What happens if a shipment is routed to Brazil’s Red or Gray customs channel?
A Red channel routing means the shipment undergoes both documentation review and physical inspection before release, while a Gray channel routing is reserved for shipments where customs suspects fraud or under-invoicing and can trigger a deeper investigation.
Do all telecom products need ANATEL certification to enter Brazil?
Products classified as telecommunications equipment, connected devices, network infrastructure, and similar ICT categories generally require ANATEL certification, and as of the May 2026 rule change, that certification number must also appear in the shipment’s customs documentation.
Can a foreign company import into Brazil without a local presence?
A foreign company can work through a local importer of record or authorized representative that already holds RADAR registration, rather than establishing its own Brazilian legal entity solely to import goods.

Shadow AI and AI-SPM: How to Close the AI Discovery Gap

What Is DDoS Protection, and Why Are DDoS Mitigation Services Moving to the Network Edge?

What to Look for in a Micro Coil Manufacturing Partner for Catheter-Based Devices

-
 Business Solutions2 years ago
Live Video Broadcasting with Bonded Transmission Technology
-
 Business Solutions1 year ago
The Future of Healthcare SMS and RCS Messaging
-
 Business Solutions2 years ago
2-Way Texting Solutions from Company Message Services
-
 Business Solutions2 years ago
Communication with Analog to Fiber Converters & RF Link Budgets
-
 DSRC Communication1 year ago
The Crossroads of Connectivity: DSRC vs. C-V2X Technologies in Automotive Communication
-
 Business Solutions2 years ago
Wholesale SMS Platforms with OTP Services
-
 Business Solutions2 years ago
Choosing the Right B2B Digital Marketing Agency: A Guide
-
 3D Technology1 year ago
How Multispectral Cameras Advance Book Scanning